Uncategorized
The Futility of Endless AI Reviews: Why AI Reviews Never Feel Finished
I think many of us are using LLMs the wrong way. Not because the tools are bad. Because…
Enterprise software. Since 1993.
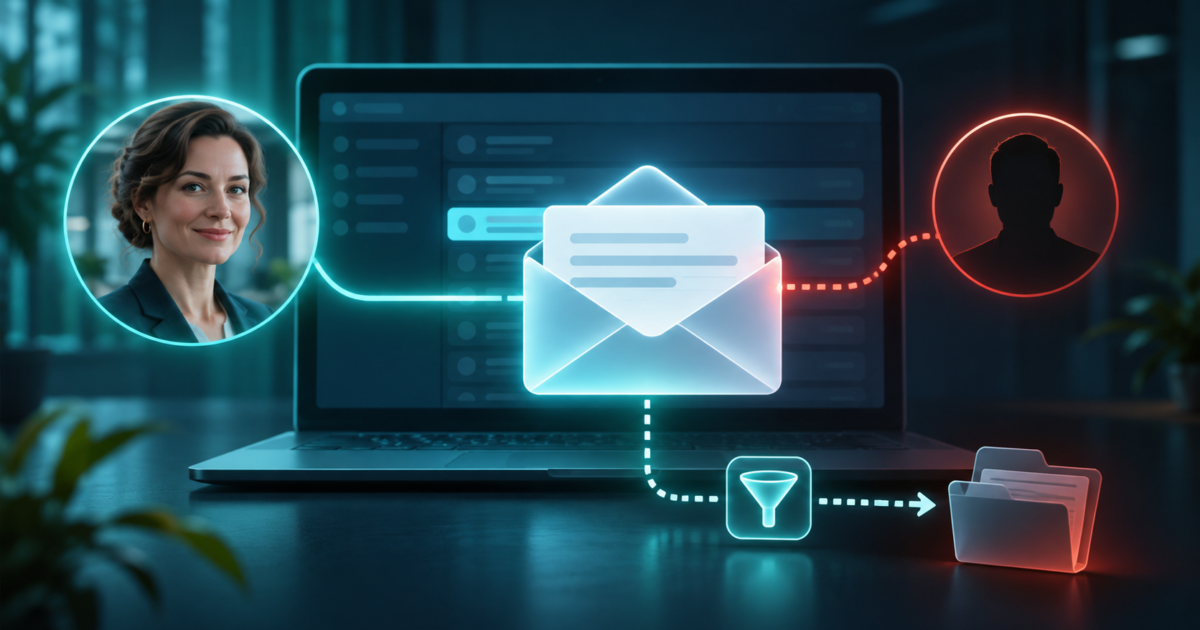
Lessons from a Microsoft 365 incident investigation: device-code phishing, a hidden inbox rule, and a phishing campaign sent from a genuine business mailbox.
Most phishing defences are built to catch a fake sender: the lookalike domain, the spoofed display name, the failed SPF check.
But what happens when the sender is real?
We recently investigated an incident where an attacker took over a legitimate Microsoft 365 mailbox and used it to send phishing emails to colleagues, partners and customers. Every message passed authentication, because every message really did come from the organisation’s own domain.
The suspicious activity was spotted and contained quickly. Our Anadata team then carried out a full Digital Forensics and Incident Response (DFIR) investigation to reconstruct exactly what happened. Here is what we found, and what every Microsoft 365 organisation can learn from it.
Days passed between the initial access and the campaign. That gap is typical: attackers often wait, observe and choose their moment.
Device-code authentication is a legitimate feature for signing in on devices where typing a password is impractical, such as smart TVs, CLI tools and conference-room hardware. The user is shown a code and asked to enter it at a Microsoft page.
Attackers abuse this by starting the sign-in themselves and persuading the victim to enter the code. The victim completes MFA on a genuine Microsoft page, and the attacker receives the session. No password is stolen, and nothing looks wrong to the user.
MFA is essential, but it protects the person signing in, not the flow they are signing in through.
The campaign messages looked like routine business notifications: task confirmations, document reviews, workspace invitations. They came from a known colleague or vendor, through legitimate infrastructure, with valid authentication.
SPF, DKIM and DMARC answer one question: did this message really come from this domain? They cannot tell you whether the account behind it has been taken over.
Detection therefore has to look at the behaviour of the sending account, not just its identity. A mailbox that suddenly sends a burst of messages in one session, to recipients it has never contacted, is a signal regardless of how clean the headers are.
Before the bulk sending began, the attacker created a rule to mark incoming messages as read and permanently delete them. That hides bounce-backs, replies such as “Did you really send this?”, and security notifications from the real user.
Malicious inbox rules are one of the most reliable early indicators of a compromised mailbox. Watch for:
Individually, each of these can be noise. Correlated, they tell a clear story.
The response included a credential reset, mailbox investigation, Microsoft Purview content searches to identify campaign messages, and invalidation of active sessions.
The order matters. Device-code phishing hands the attacker a token, not a password, and resetting the password does not necessarily terminate sessions or tokens that have already been issued. Treat them as two distinct containment steps, and revoke sessions as part of first response rather than as a follow-up.
A practical containment sequence:
Good forensics separates what happened from what probably happened.
The evidence strongly linked the phishing email to the device-code sign-in, but could not independently confirm that the recipient clicked the link or entered the code. Message traces confirmed that the campaign messages were delivered, but delivery is not interaction: the records could not show whether anyone opened them, clicked, or entered credentials. And the mailbox-audit records confirmed that large numbers of items were opened, but did not identify each item individually.
Stating these limits clearly is not a weakness of the investigation. It is what allows leadership, clients and partners to make decisions based on what is actually known.
This incident did not involve a sophisticated exploit. It involved a convincing email, a legitimate sign-in feature and a trusted mailbox. That combination is exactly why business email compromise remains so effective.
Identity security and email security are not separate disciplines. Strong authentication, mailbox monitoring, sound logging and a tested response plan only reduce risk when they work together.
If your organisation is dealing with a suspected Microsoft 365 account compromise, phishing incident or business email compromise, Anadata can help you investigate what happened and what to fix.
More like this
Uncategorized
I think many of us are using LLMs the wrong way. Not because the tools are bad. Because…
Uncategorized
As AI agents move from assisting users to acting on their behalf, enterprise authorization faces a question that…
Uncategorized
Blue-Green, Canary, Rolling, A/B, Shadow, and Recreate Deployments As microservices become central to modern application delivery, deployment strategy…